Cybersecurity
Integrated, Secure, Auditable: Owl Practice’s Answer to Data Rules and Client Agility
Canadian mental health technology sits on an awkward fault line. On one side are some of the strictest data-protection rules in the country: the federal Personal Information Protec
 Gavin Foss
Canadian mental health technology sits on an awkward fault line. On one side are some of the strictest data-protection rules in the country: the federal Personal Information Protection and Electronic Documents Act (PIPEDA) and, in Ontario, the Personal Health Information Protection Act (PHIPA), alongside a patchwork of provincial health-privacy statutes. On the other side are clients who now expect the same frictionless digital experience from their therapist that they get from their bank or their pharmacy. Practitioners are caught in the middle, stitching together systems that were never designed to talk to each other and absorbing the administrative cost when they do not.
That tension is not a niche IT problem. It shapes whether a clinician spends an evening reconciling intake forms or sees one more client, and whether a person seeking care trusts the platform enough to show up at all. Purpose-built software that treats regulation as a design input rather than an afterthought is beginning to show how the gap can close.
Navigating the intersection of privacy and digital care
Virtual care is no longer the exception in Canada. Recent data show that 80.8 per cent of respondents report satisfaction with virtual care options, a level of acceptance that would have been hard to imagine before the pandemic reshaped how Canadians reach their providers. The convenience is real, and for mental health in particular, the ability to attend a session from a private room at home has widened access for people who would otherwise go without.
The same research is blunt about the catch: privacy and security remain barriers for many of the people considering these services. The result is a confidence gap. Clients want the convenience, but they hesitate when they cannot see how their most sensitive information is protected. For mental health providers, who hold some of the most sensitive records in all of health care, that hesitation is not abstract. It is the difference between a prospective client booking a first appointment and quietly closing the tab.
The stakes are compounded by how unevenly organizations are prepared. Research indicates that 91 per cent of Canadian businesses actively work to comply with privacy laws, so awareness of the obligation is widespread. Yet only 64 per cent consider themselves highly prepared to respond to a data breach. That gap between intention and readiness is where sensitive information is actually exposed. For a solo practitioner or a small group practice without a dedicated security team, it is also where genuine, built-in protection stops being a compliance checkbox and starts being a competitive advantage.
The administrative toll of segmented systems
The privacy problem has a quieter twin: fragmentation. While 92 per cent of Canadian healthcare providers have access to digital health systems, only 52 per cent share information externally, according to Statistics Canada. Incompatible platforms, mismatched data formats, and well-founded anxiety about information security keep records locked inside individual tools. The clinical cost is coordination that never happens; the human cost is a practitioner re-entering the same information into three systems that refuse to acknowledge one another.
This is where the regulatory patchwork turns from a legal abstraction into a daily workflow problem. PIPEDA governs private-sector handling of personal information at the federal level, while health-specific statutes such as Ontario's PHIPA set their own rules for custodians of personal health information, and other provinces layer on their own requirements. A practitioner who sees clients across provincial lines, or who simply wants to use a mainstream scheduling or messaging tool, has to reconcile expectations that were written separately and do not always map cleanly onto one another.
Without clear technical guidance, the rational response is often avoidance. Some providers default to manual processes, disconnected tools, or paper precisely because the digital alternative feels like a liability they cannot fully assess. The outcome is more administrative burden, not less, and care documentation that is scattered rather than coherent. The promise of digital health, in other words, is routinely undone by the friction of making it compliant.
When compliance is built in, not bolted on
The alternative is software that treats the rules as constraints that shape how features work from the first line of code, rather than as a disclaimer added at the end. When data residency, consent, encryption, and access logging are part of the architecture, compliance stops competing with usability and starts enabling it. A clinician does not have to choose between a tool that is easy to use and a tool that keeps them inside the regulatory lines, because the easy path and the compliant path are the same path.
Owl Practice, a practice-management platform designed specifically for Canadian mental health professionals, is one example of this approach in practice. Built for Canadian providers rather than adapted from a generic global product, it emphasizes Canadian data residency and folds PIPEDA and PHIPA considerations into the infrastructure instead of leaving each practitioner to assemble their own compliant stack. The design philosophy is straightforward: regulatory requirements are design constraints, and when they are honoured at the architecture level, security and usability advance together rather than at each other's expense.
That framing matters because it inverts the usual trade-off. In most tools, every security feature feels like friction added on top of the work. When the constraints are foundational, the same features become the reason the software is pleasant to use at all, because the practitioner never has to leave the system to do something safely.
Reclaiming time through secure portals
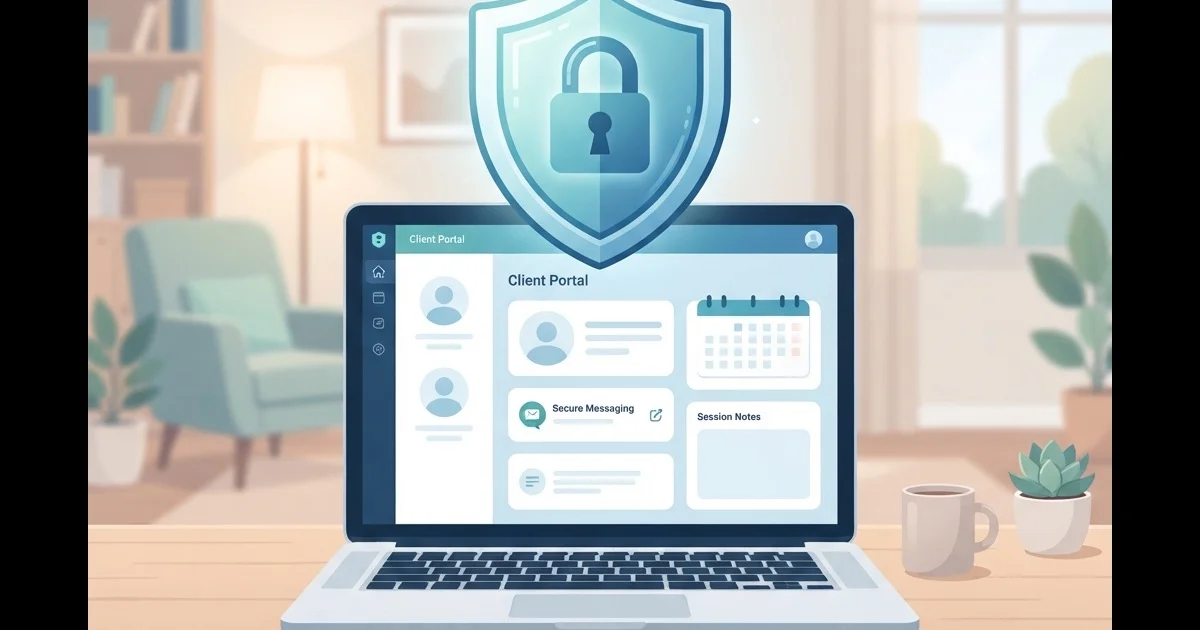
The clearest test of that philosophy is the client-facing portal, where privacy and convenience meet most directly. A secure client portal gives clients a self-service environment available around the clock, where they can book appointments, complete intake forms, and message their therapist without the provider bolting on third-party tools of uncertain compliance status. Consent forms with electronic signatures live inside the same system, which removes the separate document-management workarounds and the physical paperwork that slow intake to a crawl.
Secure messaging does the same job for communication, replacing the non-compliant email threads that practitioners fall back on when nothing better is available. Messages stay inside an auditable, encrypted system with detailed access logs, and retention policies and permissions are managed automatically in line with compliance standards, with documents kept under the practitioner's control. For the client, the experience feels like the responsive, modern booking software they expect from any other service. For the practitioner, it stays inside regulatory boundaries without demanding constant vigilance. That is the compliance-convenience gap closing in a single feature.
Managing complex schedules safely
Calendar management shows the same attention to the balance. One-way synchronization with Google, Apple, and other scheduling platforms lets a practitioner display real-time availability while keeping client-identifying details from being exported to external services. It is a small design decision with outsized consequences: standard calendar integrations routinely leak protected health information through shared calendars or sloppy synchronization settings, and one-way sync closes a vulnerability that most practitioners never knew they had.
The operational features follow from the same logic. Automated appointment reminders cut no-show rates through encrypted delivery channels that hold the privacy line, and multi-room coordination prevents double-booking across group practices without anyone maintaining a spreadsheet of who is where. These are the logistics that quietly consume administrative hours. Handing them to a system that was built to handle them compliantly gives practitioners their attention back for the clinical work that actually requires it.
Building a resilient future for mental health care
None of this makes compliance effortless, and no platform removes a practitioner's professional responsibility for the data they hold. What purpose-built software can do is change the default. When the compliant option is also the convenient one, providers adopt digital tools with confidence instead of avoiding them out of caution, and the administrative drag that pushes clinicians toward burnout eases rather than grows.
As Canadian health care continues its slow, uneven digital transformation, the organizations that thrive will be the ones that stop treating privacy and user experience as opposing forces. The regulatory rigour is not going away, nor should it. The question is whether the tools practitioners rely on are built to honour that rigour and the experience their clients expect at the same time. Increasingly, the ones that are will be the ones left standing.
About the author
Gavin Foss
Gavin Foss is the editor-in-chief at Tech Forum, covering the Canadian technology landscape with a focus on AI and emerging technologies. His technical depth and industry connections make him one of Canada's most respected tech journalists.
Keep reading
More from Tech Forum
Nesto CAD 302M Series E Funding Closes
Explore a detailed, data-driven analysis of Nesto's CAD 302M Series E funding and its significant impact on the Canadian mortgage tech landscape.
Steph Moreau / October 7, 2026
Fields Medalists vs OpenAI's 722 AI Math Manuscripts
OpenAI posed ~4,000 problems to get 372 result families and published 722 manuscripts, eight days after an IAS advisory group asked labs to stop testing advanced mathematics on proprietary models.
Steph Moreau / October 7, 2026
Chexy CAD 14M Series a Toronto
Chexy CAD 14M Series A Toronto: Toronto's innovative fintech secures CAD 14M in funding spearheaded by Khosla Ventures, supported by Air Canada.
Derek Fung / October 6, 2026